

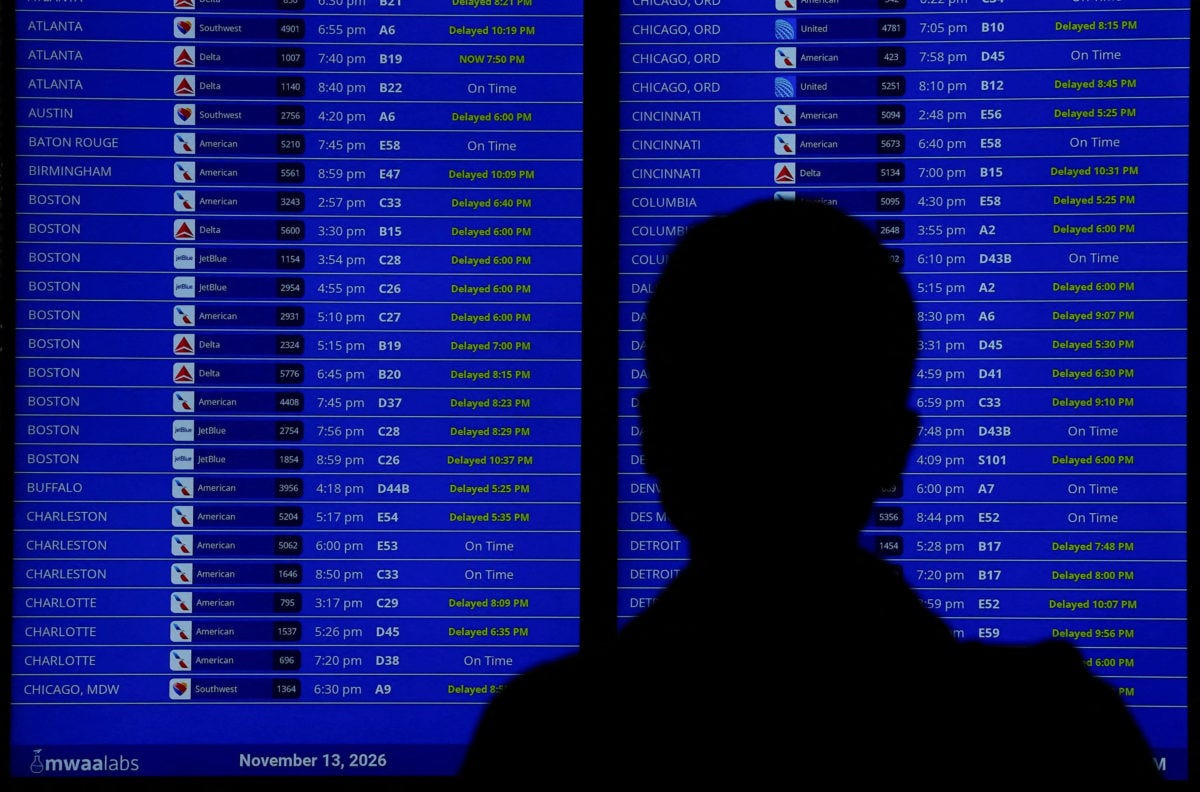
It seems like the perfect storm. Microsoft reports and outage, FAA orders a ground stop, Apple has issues, the NSA’s messaging system goes down, United Airlines has issues, Google has issues...
As a third aircraft carrier arrives within striking range of Iran, it is certainly reasonable to wonder whether Iran has decided to demonstrate some of their, er..., capabilities.
The media isn’t helping. Government officials like Transportation Secretary Sean Duffy and Homeland Security Secretary Markwayne Mullin claim this isn’t an AI orchestrated attack, just things breaking as they are being updated. The media seems credulous as all of this is happening all at once - unlike in the past. The frontier labs (Anthropic and Open AI) are only making things worse with their fear mongering.
So, let’s settle what we can in this space.
AI and adversarial cyber
Let’s get back to basics. Software is written in programming languages. But the computer does not execute source code - it executes machine code. The step in between is a compiler.
The machine code are the bits and bytes of files that have endings like ‘.exe’ and ‘.dll’. (I’ll just limit myself to oversimplifying Windows right now. There are other file formats for machine code.) These are not human readable like source code. They do represent a certain semantics of the machine. For example, a ‘process’ (the area in memory where the machine code is running) opens a ‘handle’ to a ‘file’ on the ‘hard drive’. That file is then sent to a ‘buffer’ (an area of memory) on a printer. The printer then prints the file onto paper.
AI is now able to infer these semantics from machine code. That, then, isolates a set of possible attacks that can be tried. The way a program handles computer memory is the most common target. Another approach - and this is something people have tried since programs were compiled - is reverse compiling back to source code.
In this instance, the verbatim source code itself is not so much the goal as the use of certain patterns that are known to produce vulnerabilities. The ability to reverse engineer a machine code binary to that point has been a very high level skill requiring lots of compute resources and time.
AI has flattened the learning curve and compressed the “time-to-exploit.” An adversary no longer needs high level skills or huge compute resources. And the time required to go from inferring likely vulnerabilities, discovering, and then exploiting them has dropped dramatically.


Red Teams and the subsequent patches
If we assume this to be the case, then we have to get in front of it by staffing “red teams” and equipping them with the latest frontier model capabilities. These red teams then attack a target as would an adversary to discover where the target technology needs improvement. This is nothing new. What is new? First, AI is identifying significantly more new vulnerabilities horizontally across the tech stack (operating systems, databases, web application hosting, browsers, etc.) as well as vertically in any given part of the stack. Second, we used to be able to spend a week or two testing the patches for these new vulnerabilities.
We simply do not have that kind of time anymore. It is the devil you know (test and field patches quickly and risk breaking things) or the devil you don’t (take a week or two to test more robustly and hope an adversary doesn’t beat you to it). The devil you know causes inconvenience. The devil you don’t causes…? Well, that’s just it; you don’t know.
The sheer volume of patches being released all at once is most likely why so many things are breaking all at once. Consider Microsoft (if only because of how pervasive its products are): It has a monthly patch cycle. The second Tuesday of every month is known across the tech world as “Patch Tuesday.” That was November 10th. It was that week that this cascade of outages began to hit. Vendors will also occasionally issue out-of-cycle patches for especially critical discoveries. (Java4Shell/CVE-2026-114938 prompted Oracle to issue an out-of-cycle patch.)


This is the nuance the media misses. This is probably not something where AI is orchestrating attacks. But AI is definitely in the mix here because of how it flattens the learning/time-to-exploit curve.
Cybersecurity has been like swimming in four-foot seas. Now we have to learn how to surf a fortry-foot wave - like... yesterday.